By Rivell Editorial Team · Published 2026-08-26
Cybersecurity services for New Jersey businesses can combine threat detection, endpoint protection, network security, cloud security, patch management, incident response, compliance support, security awareness, reporting, and backup and recovery coordination within a documented scope.
What should New Jersey businesses compare in cybersecurity services?
New Jersey businesses should compare cybersecurity providers by documented service scope, monitoring and escalation procedures, endpoint, network, and cloud protection, incident-response responsibilities, backup and recovery coordination, compliance support boundaries, and reporting.
How does monitoring support earlier detection and escalation?
Where monitoring is included in the contracted scope, configured signals from networks, systems, endpoints, and cloud services can be reviewed under documented triage and escalation procedures. Coverage depends on connected tools, telemetry, access, contacts, severity, and response responsibilities; it does not guarantee every threat will be detected or contained immediately.
Why do New Jersey businesses need routine backups and disaster recovery?
Recoverability after ransomware or another disruption depends on which systems and data are protected, whether usable recovery points remain, how often backup integrity and restore procedures are tested, and the conditions of the incident. The CISA #StopRansomware Guide recommends offline, encrypted backups and regular testing of backup availability and integrity. Buyers should ask whether backup, restore testing, incident response, and recovery coordination are included in the same scope or assigned to separate providers.
How does small business cyber security work?
Small business cyber security can combine risk management, ongoing monitoring, incident response, endpoint, network, and cloud protection, backups, and security awareness within a defined service scope. No control guarantees prevention or regulatory compliance.
What does a small business cyber security plan include?
A small business cybersecurity plan can begin with a technical risk review that documents gaps in network design, endpoint coverage, cloud configuration, patch management, backup procedures, access controls, and response responsibilities. The agreed service scope can then connect appropriate monitoring, protection, reporting, and recovery coordination. Managed IT and cybersecurity services NJ providers should document which responsibilities they own and which remain with the customer or another vendor.
How do New Jersey businesses implement managed cyber protection?
Small business cyber security in New Jersey typically follows a structured deployment process:
- Risk assessment — Consultants review the existing environment, identify gaps, and document the technical scope; the organization and qualified advisers determine which legal, regulatory, contractual, or insurance obligations apply.
- Tool deployment — Providers deploy the endpoint, network, cloud, access, and monitoring controls included in the agreed scope.
- Ongoing monitoring — Where included in scope, monitoring follows the connected tools, telemetry, access, contacts, severity, and documented response responsibilities.
Managed cyber protection can connect network security, cloud security, endpoint protection, patch management, incident response, and data backup for New Jersey organizations within an agreed scope.
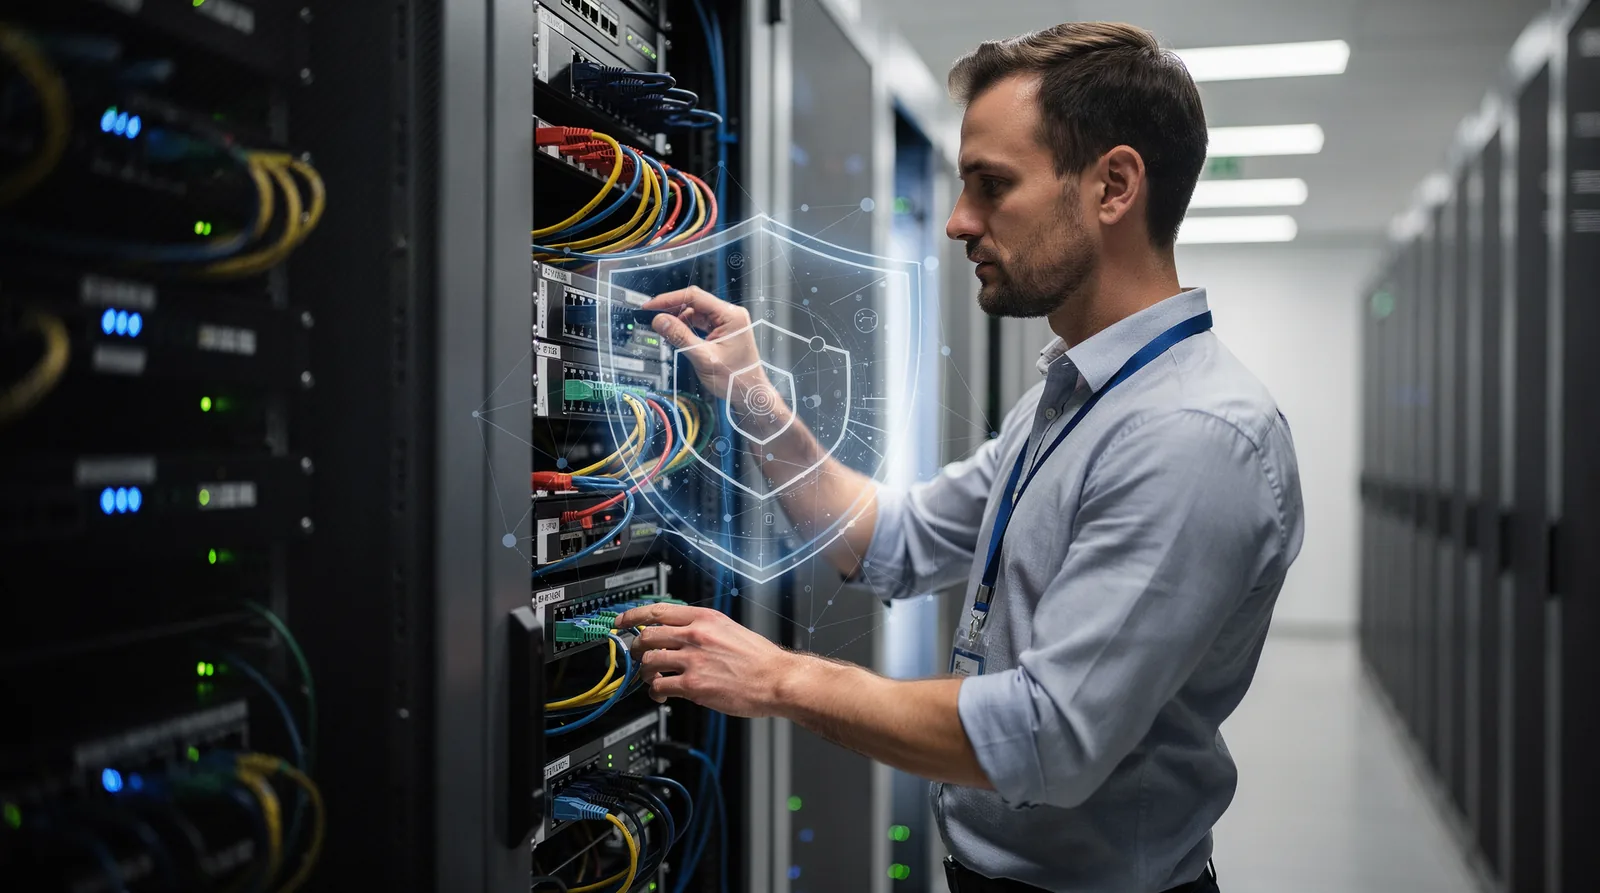
Managed cybersecurity services connecting endpoint, network, cloud, incident response, and backup controls
What does managed cyber protection include?
Managed cyber protection can coordinate risk reviews, endpoint protection, network security, cloud security, patch management, monitoring, incident response, reporting, security awareness, and backup and recovery support under a documented scope.
How does managed protection differ from basic antivirus?
Antivirus is only one control. The NIST Cybersecurity Framework (CSF) 2.0 organizes cybersecurity risk management across Govern, Identify, Protect, Detect, Respond, and Recover. A provider comparison should document which activities, systems, and response decisions are included under each function instead of treating any single tool or monitoring service as complete protection.
What specific services fall under managed cyber protection?
- Risk management — reviewing and documenting technical vulnerabilities and treatment priorities
- Incident response — coordinating documented triage, escalation, containment, remediation, and communication responsibilities
- Network security improvements — hardening firewalls, endpoints, and access controls
- Business continuity planning — supporting documented recovery priorities and responsibilities
- Disaster recovery — restoring data and systems from verified backups
Rivell supports organizations in sectors including healthcare, finance, legal and professional services, manufacturing, education, and small business. The service scope should reflect each organization’s systems, users, data, risk, and operating requirements.
How to compare cybersecurity providers in New Jersey
Ask each provider to document what is included, excluded, and assigned to the provider, the customer, or another vendor. Compare proposals using the same questions:
- Service scope: Which users, devices, networks, cloud services, locations, and third-party systems are covered?
- Monitoring and escalation: Which tools and signals are connected, when are alerts reviewed, who is contacted, and what happens at each severity level?
- Endpoint, network, and cloud protection: Which controls are deployed, maintained, reported on, and excluded?
- Incident response ownership: Who handles triage, containment, remediation, recovery, communications, and coordination with insurers or advisers?
- Backup and recovery: Which systems and data are included, how are backups tested, and who owns restoration decisions?
- Compliance boundaries: What technical controls and documentation can the provider support, and which obligations remain with the organization and qualified advisers?
- Reporting and contracts: What evidence, review cadence, exclusions, dependencies, and contract terms are documented?
Cybersecurity services FAQ
Does managed cybersecurity prevent every incident?
No. Security controls can reduce risk and support earlier detection, documented escalation, response, and recovery, but they do not guarantee prevention, complete detection, or immediate containment.
What should a monitoring scope define?
It should identify the connected tools, available telemetry, systems and users covered, access requirements, contact paths, severity rules, review periods, escalation steps, and response responsibilities.
Who determines a business’s compliance obligations?
The organization and its qualified legal, regulatory, contractual, insurance, or other advisers determine applicable obligations. A cybersecurity provider can help identify technical gaps and support the implementation and documentation of agreed controls.
Conclusion
New Jersey businesses evaluating cybersecurity services should compare documented scope, monitoring coverage, escalation ownership, endpoint and network controls, cloud security, backup and recovery coordination, security awareness, reporting, and contract exclusions. Rivell has supported New Jersey organizations since 1997 and provides customized cybersecurity services connected to the systems, users, devices, cloud services, backups, and support processes each organization relies on. Buyers should review the proposed scope and evidence rather than relying on guarantees. Review Rivell testimonials and case studies when evaluating provider evidence.